Self-hosting

4631 readers
1 users here now

Hosting your own services. Preferably at home and on low-power or shared hardware.

Please don't share vibe coded projects here.

Also check out:

founded 4 years ago
MODERATORS
1


Beneath the dark and uncertain clouds of bigtech, hidden among the declassed byte workers and the false technological prophets who with siren songs offer their digital services to "facilitate" digital life, rises an anarchic and countercultural community that seeks to reclaim the Internet and fight against those who squeeze our identity in the form of data to generate wealth and advertising for mass social manipulation and cohesion. Navigating the network of networks, with a small fleet of self-managed servers, geographically distributed yet cohesively united by cyberspace, the self-hosting community emerges as a way of life, a logic of inhabiting the digital, a way of fighting for an open, human network, free from the oligarchy of data.

To the naturalization of the already crystallized phrase "the cloud is someone else's computer" we add that this "someone else" is nothing more than a conglomerate of corporations that, like a hungry kraken, devours and controls the oceans of cyberspace. Against this we arm ourselves in community action, direct and self-managed by and for those of us who inhabit and fight for a more sovereign and just Internet. Our objectives are clear, and our principles are precise. We seek to break the mirage and charm that these beasts imposed at the point of ISPs and blacklist and we promote the ideal of an organized community based on their computing needs without the intermediation of outlaws and byte smugglers.

The big tech companies disembarked on the net with a myriad of free services that came to replace standards established during years of work among users, developers, communities, technocrats and other enthusiasts of the sidereal tide of cyberspace. By commoditizing basic Internet services and transforming them into objects of consumption, they led us to their islands of stylized products, built entirely with the aim of commercializing every aspect of our lives in an attempt to digitize and direct our consumption. Sending an email, chatting with family and friends, saving files on the network or simply sharing a link, everything becomes duly indexed, tagged and processed by someone else's computer. An other that is not a friend, nor a family member, nor anyone we know, but a megacorporation that, based on coldly calculated decisions, tries to manipulate and modify our habits and consumption. Anyone who has inhabited these digital spaces has seen how these services have changed our social behaviors and perceptions of reality, or will we continue to turn a blind eye to the tremendous disruption that social networks generate in all young people or the absurd waste of resources involved in sustaining the applications of technological mega-companies? Perhaps those who praise the Silicon Valley technogurus so much do not see the disaster of having to change your cell phone or computer because you can no longer surf the web or send an email.

If this is the technosolutionism that crypto-enthusiasts, evangelists of the web of the future or false shamans of programming offer us, we reject it out of hand. We are hacktivists and grassroots free software activists: we appropriate technology in pursuit of a collective construction according to our communities and not to the spurious designs of a hypercommercialized IT market. If today the byte worker plays the same role as the charcoal burner or workshop worker at the end of the 19th century, it is imperative that he politicizes and appropriates the means of production to build an alternative to this data violence. Only when this huge mass of computer workers awaken from their lethargy will we be able to take the next step towards the re-foundation of a cyberspace.

But we do not have to build on the empty ocean, as if we were lost overseas far from any coast; there is already a small but solid fleet of nomadic islands, which dodge and cut off the tentacles of the big tech kraken. Those islands are the computers of others, but real others, self-managed and organized in pursuit of personal, community and social needs. Self-hosting consists of materializing what is known as "the cloud", but stripped of the tyranny of data and the waste of energy to which the big tech companies have accustomed us. They are not organized to commoditize our identities, but to provide email, chat, file hosting, voice chat or any other existing digital need. Our small server-islands demonstrate that it is possible to stay active on the network without the violent tracking and theft, nor the imposed need to constantly replace our computer equipment: the self-hosted services, being thought by and for the community, are thought from the highest possible efficiency and not the immoral waste that directly collaborates with the climate crisis.

For this reason, we say to you, declassed byte workers, train yourself, question yourself, and appropriate the tools you use in order to form a commonwealth of hacktivists! Only between the union of computer workers and the communities of self-hosting and hacktivism we will be able to build alternatives for the refoundation of a cyberspace at the service of the people and not of the byte oligarchy.

But we need not only the working masses but also ordinary digital citizens, let's wake up from the generalized apathy to which we have been accustomed! No one can say anymore that technology is not their thing or that computing does not matter to them when all our lives are mediated through digital systems. That android phone that is still alive but no longer allows you to check your emails or chat with your family is simply the technological reality hitting you in the face; as much as the anxiety or dispersion that has existed in you for the last 15 years. Imagine the brain of a 14 year old teenager, totally moth-eaten by the violent algorithms of big tech!

Community digital needs are settled on the shores of our server-islands, not on the flagships of data refineries. Let's unite by building small servers in our homes, workplaces or cultural spaces; let's unite by building data networks that provide federated public instant messaging services that truly respect our freedoms and privacy. Let's publish robust, low-latency voice services; let's encourage the use of low computational consumption services to democratize voices whether you use a boat or a state-of-the-art racing boat. Let's create specialized forums and interconnect communities to unite us all, let's set our sails with the protocols and standards that exist, which allow us to dive the network using the device we want and not the one imposed on us. Let's lose the fear that prevents us from taking the first step and start this great learning path, which as an extra benefit will make us regain not only our technological sovereignty but also the control of our digital essence. It is not a matter of cutting off the private data networks of big tech but rather of building self-managed, self-hosted and self-administered spaces from the hacktivist bases, together with the workers of the byte and the digital citizenship: an Internet of the community for the community.

2


Once you know how it works, managing containers manually with crun is pretty easy. But if you don't want to do everything manually, the next best thing is podman.
But podman pulls already around 500 MB in dependencies on Alpine, while half of it's features don't work without Systemd and the other half duplicates system-interfaces on a local website.

Which is why, before i create my own scripts, anything that let's you with a single command

  • create container from template
    • add sub-uid:gid
    • add respective default nftable rule
  • same for deleting container
  • list contianers by status

Things like that?

3
4


cross-posted from: https://lemmy.blahaj.zone/post/47815424

Portainer is changing to a mostly AI and kubernetes supported app.

5


cross-posted from: https://piefed.ca/c/selfhosted@lemmy.world/p/957754/local-homeserver-suddenly-not-responsive-to-ssh-but-can-be-pinged

Cross-posting this from Lemmy world where it seems my post coming from piefed.ca is not federating.

This is something that seems to happen randomly to my little RaspberryPi 4B homeserver, like once every few months maybe.

What happens is that out of nowhere (meaning I didn't make any change to config or installation) I cannot reach any services I host on it (i.e. Jellyfin, Anchor notes...). I cannot access it via SSH at all, connection keeps timing out.

Ping however gives a signal. I can see/hear its running and doing something, since I hear the external HDD working. It is running headless and I have no monitor and/or keyboard I could connect.

So far my only way out is to just switch its power off, which is obviously not good for the hard drive. It has happened now like half a dozen times over the past few years, so I am wondering what a better way is to handle this. This was on RPI OS and now its happening on DietPi, so seems not related to the OS version.

I tried sending a shutdown signal via SSH but that also just times out, so how do I get it to shutdown properly?

Secondly, what kind of logs could I look at or start collecting to make sense of this?

6
7


This is a little bit of a wall of text but I hope it will be a nice sample for such a setup.

8
9
10


cross-posted from: https://discuss.tchncs.de/post/66988984

What I have

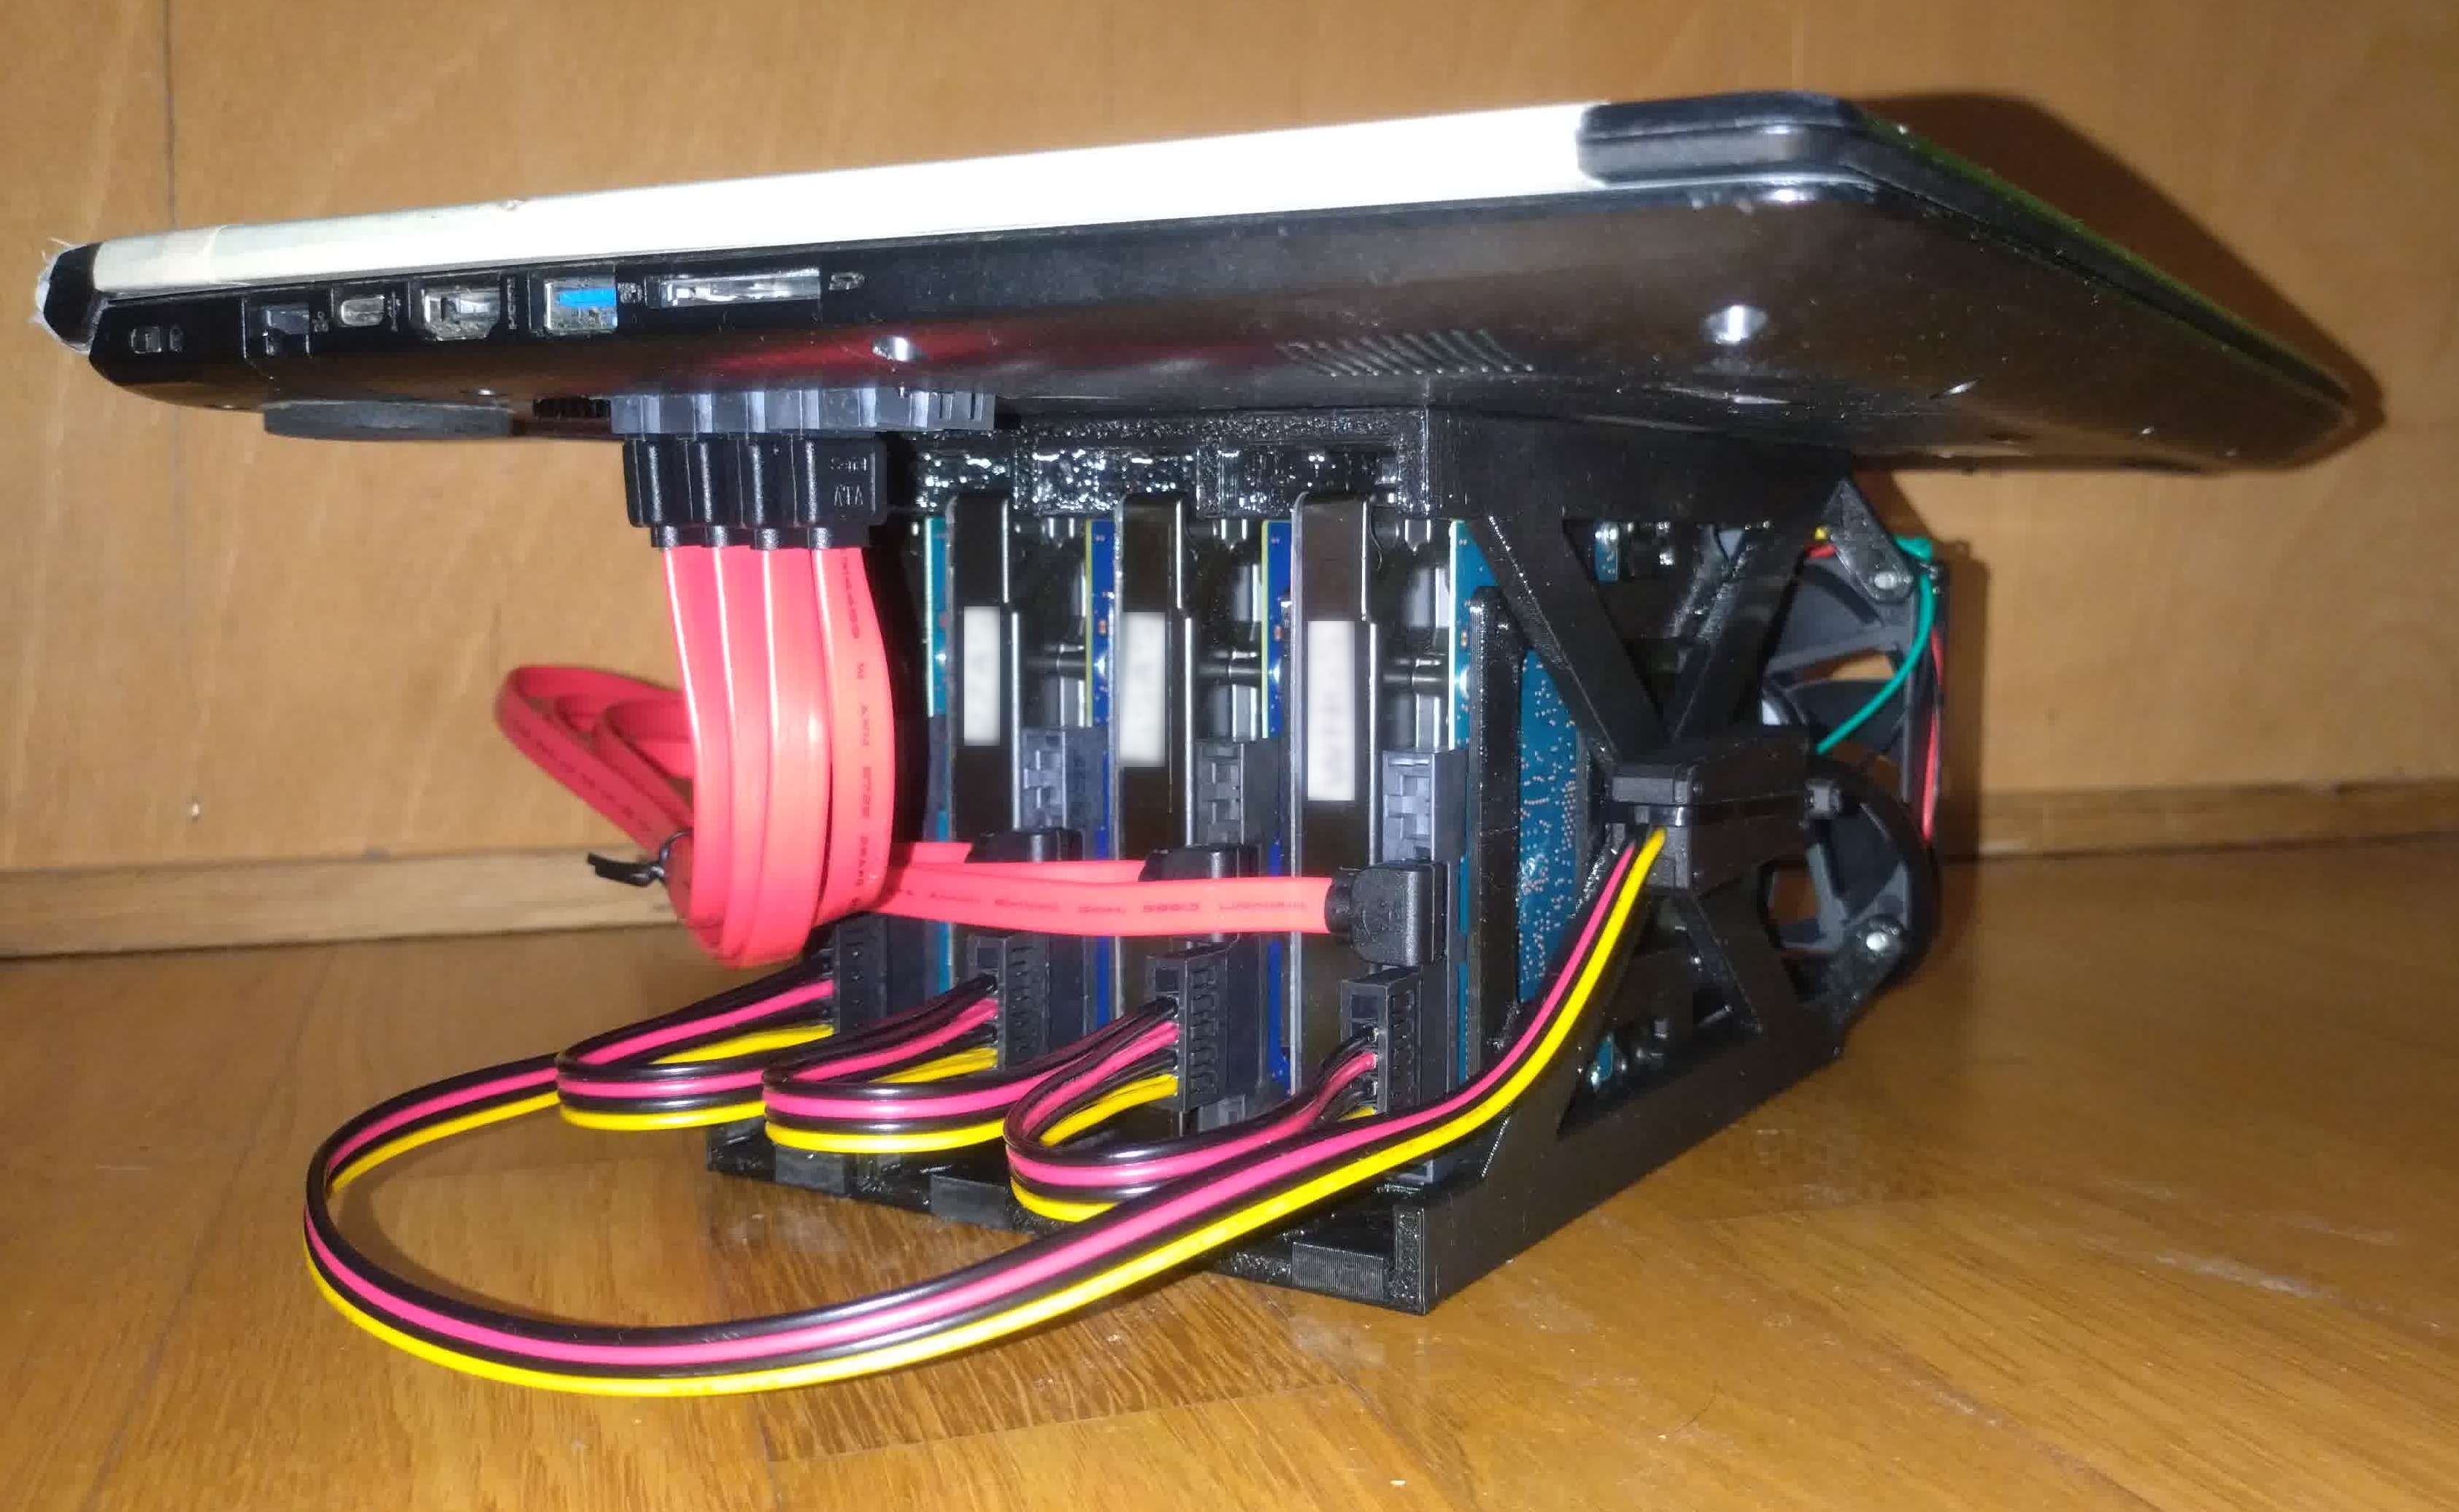
I have an old Acer Aspire A515-51G and I also have a desire to have a home server. In combination this creates a need for the laptop to carry more HDDs than it can from factory. Usually it can take one M.2 SSD and one 2.5" SATA drive.

What I want

I want to make the laptop able to run at least 4 HDDs in RAID 5 for storage and have one SSD as boot drive.

What I did

The buying phase

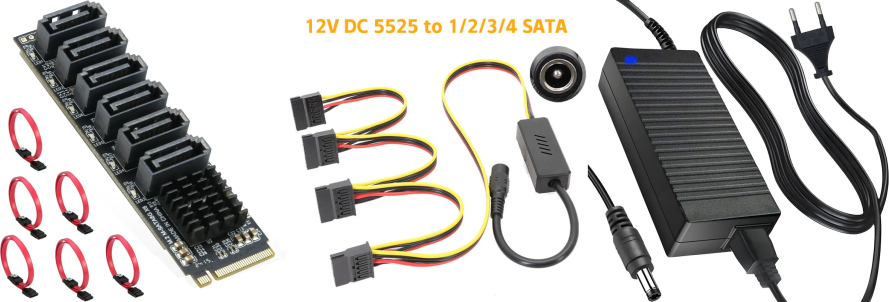
  • 4 HDDs
  • M.2 to SATA adapter
  • 12V/5V SATA power converter
  • 12V 10A power supply

The designing phase

I needed space to hold the HDDs, so I designed a 3D printed a cage to attach to the bottom of my laptop. Two 80mm fans can be attach to it. You can see it on printables. Also I remixed a tray (here is the original) so the HDDs can slide in and out of the cage.

.

The assembly phase

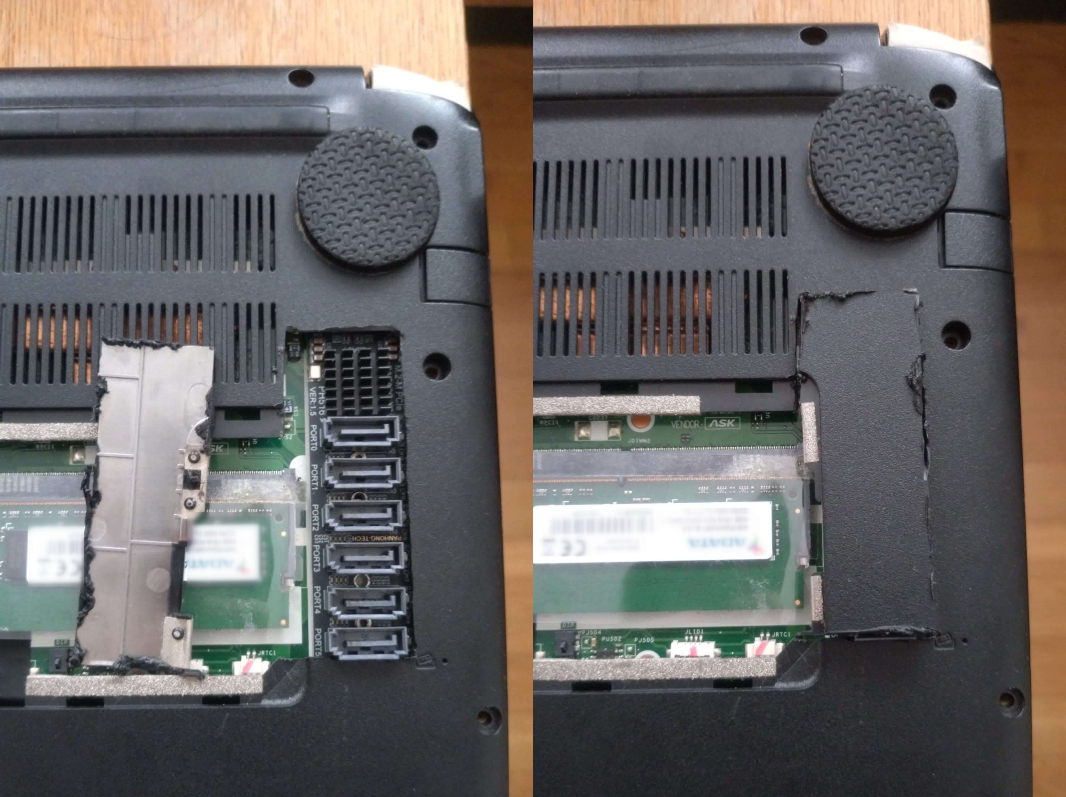
A cutout at the bottom of the laptop was needed to give access to the SATA ports of the adapter.

I put a 2.5" SSD into the already present place for it in the laptop.

Then the cage was attached to the laptop, the HDDs were put in their trays, the trays inside the cage and the cables attached to the adapter and HDDs.
11
12
1
submitted 2 months ago* (last edited 2 months ago) by tofu@lemmy.nocturnal.garden to c/selfhosting@slrpnk.net


Cross posted from: https://lemmy.nocturnal.garden/post/814241

Paperless-ngx is an extensive document management system. 3.0.0 has just been released.

It seems from a user/admin perspective that a lot of obsolete stuff under the hood got removed and they did some performance stuff, but it's also full of AI features. There's too many changes to read them all though, I wonder if there's a blogpost or something somewhere summarizing the main changes.

Personally I'll stay with 2.X for some days at least to see what people say about the new version. I'm not interested to have AI parse my documents, the alrogirthmic auto tagging etc works quite well.

13


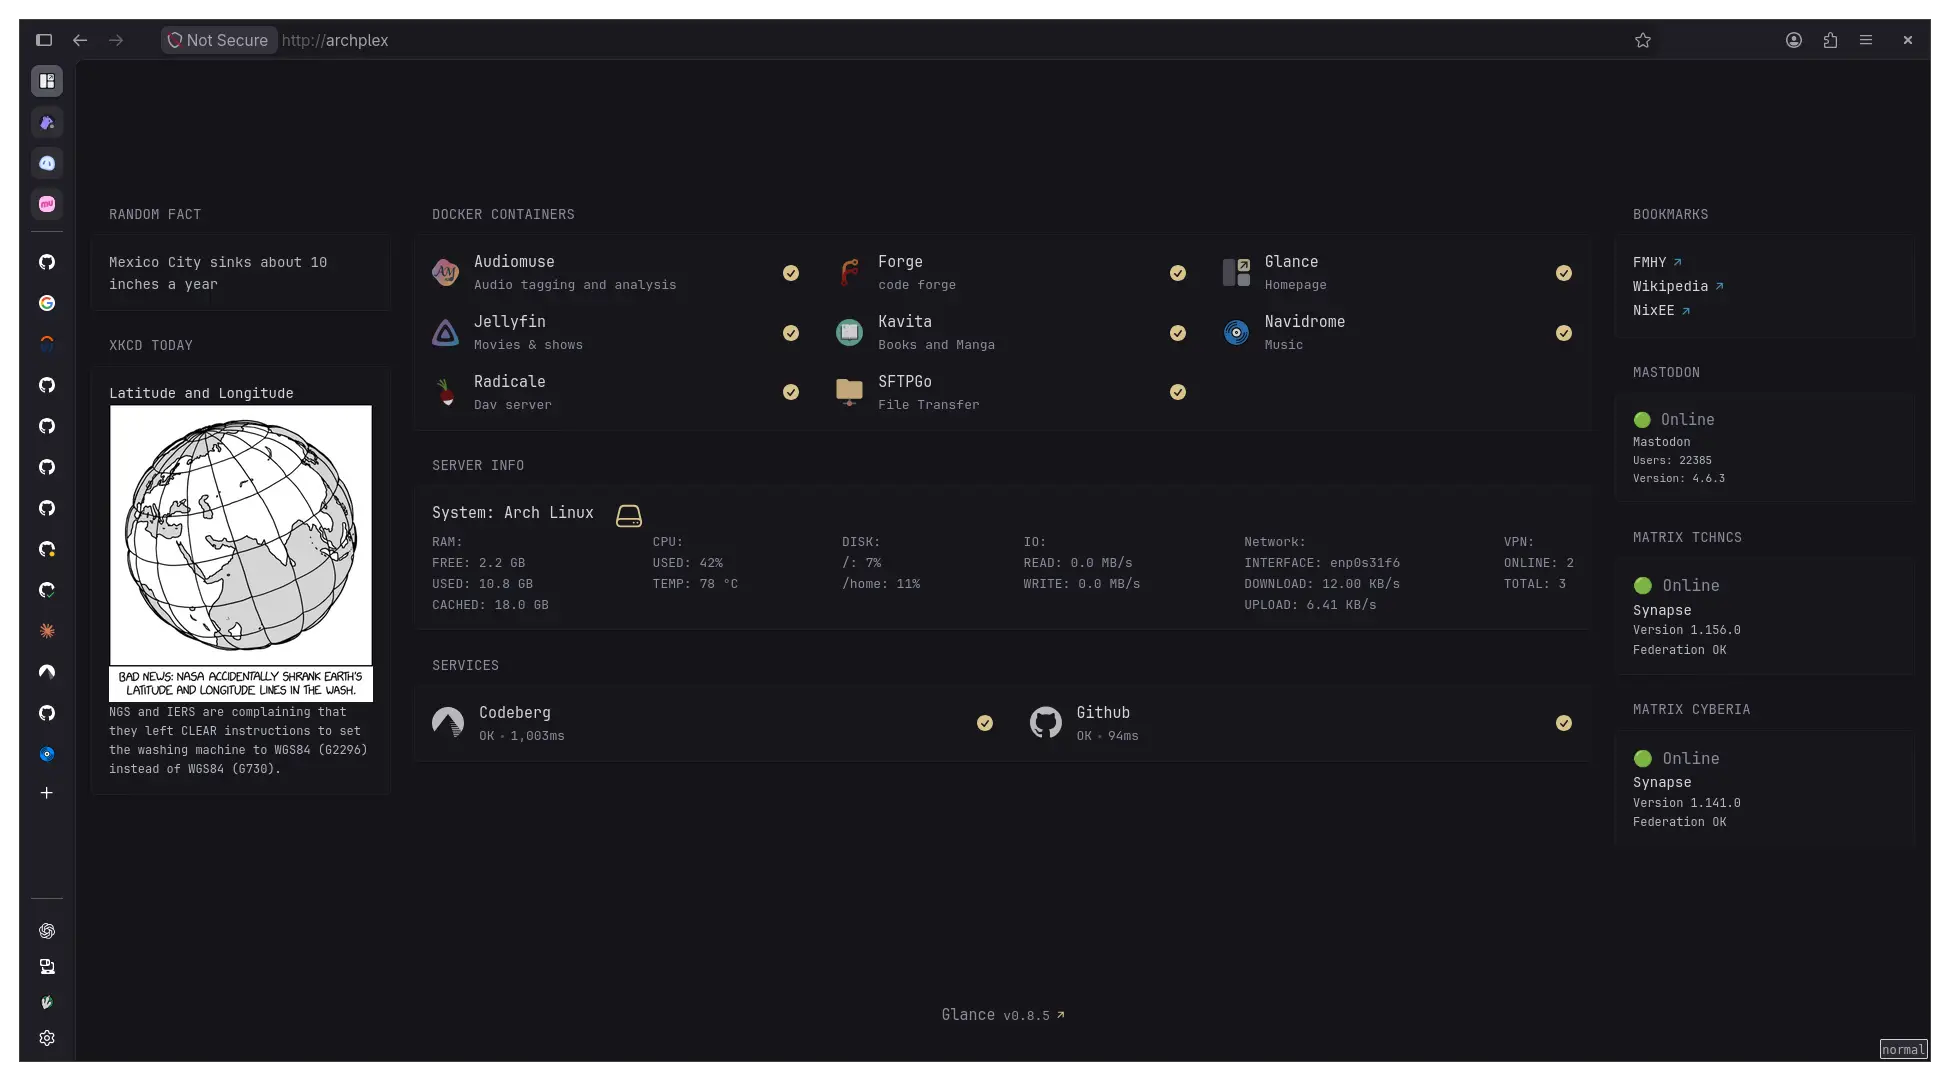
Cross-posted from "My selfhosting setup so far" by @innocentz3r0@programming.dev in !selfhosted@lemmy.world


Hey everyone! I'm sort of still green for selfhosting, but I wanted to share my setup so far:

The following services are selfhosted in docker

  • Audiomuse (smart music tagging, mood based and all that)
  • Navidrome for music hosting
  • Jellyfin for TV shows (not a lot) and Films (not a lot again, but steadily increasing)
  • Radicale for serving contacts/TODOs/calendar
  • SFTPGo to act as my drive
  • Kavita for ebooks and manga (I have tons of both)
  • Glance for homepage
  • forgejo for git forge hosting

The system specs are kind of visible in the homepage, so I won't spell them out here again. Mostly an old optiplex running arch, though I want to change it to nixos later on.

System tools:

  • nushell for shell
  • calibre for ebook management and tagging + fanficfare plugin to download fanfictions
  • Caddy for reverse proxy (so I don't have to remember ports)
  • netbird for VPN (also because it allows me to set wildcard DNS resolution for nodes, so I don't have to set up a dedicated pi-hole or adguard)
  • Handbrake and ffmpeg for processing videos and such
  • beets for tagging music
  • a sysinfo script to generate system information for glance to consume
  • Probably other things too, I'm forgetting

Everything is accessible only via netbird, and external inbound connections are firewalled off

Apart from that, I eventually plan on adding the following as well:

  • Immich for photo hosting
  • Vaultwarden for passwords
  • Gollum (still debating on alternatives) for a webUI for my notes
  • Paperless-NGX

I'm still thinking on more that I can add. Note that whatever I add should not need an inbound connection/stable IP address, since I don't intend to expose the server to the public. Any suggestions/tips? Thanks!

UPDATE: Forgot to add, I'd probably add homebox too, for inventory management 😅

UPDATE 2: I'm silly, I forgot that I'm also looking into self-hosted RSS feed readers 😆

14
15
16
17
18


Flohmarkt is a federated classified ads software.

19


forgive the tyos, english is absolutely my first language but we strugglin over here, ya feel? or, take it as confirmation this ain't some damn clanker bullshit

It's just like holy shit! this is what I've wanted my music to do my whole life! This is almost just another member of the family.

Feishin and the smart playlists really really shine when adding user ratings into the mix. plus, adding a "mood" tag and then being able to use our own terms, it is incredible.

Build a custom station with the tags you want, then add "not played in the last days" (depending on how much traffic/supply of that particular kind of music gets) and it keeps it fresh. Add in "rating is not 1" and you'll see the stuff that hasn't been rated yet, but it won't even let 1 start tracks into the queue!

I have rediscovered old favorites, found new songs by classic artists, have perfectly curated playlists down to the nth degree, custom stations that show me exactly what i want before i even knew i wanted to listen to that right then, all without commercials, on every device i own.

i am pumped for the future of the open subsonic API's! I think a skipped count could be awesome. I'd like to automate some stuff based off skip counts.

the navidrome plugins are getting some inertia, i am excited to see where that goes.

Other Navidrome/opensubsonic users, how do you guys use the 5 stars? for me it is

  • 5 amazing song, not only will i 99% of the time never skip it, i will try to get everyone's attention and have them listen
  • 4 i really like this song and have stopped what i am doing to pay attention to it, it is not likely but may get skipped depending on the mood/genre desired at that time
  • 3 - this song is good and i notice it and smile while continuing doing my thing, unless it is the wrong mood/genre (can i blast it while working?), which means it gets skipped.
  • 2 - this song is unobtrusive and doesn't appear to bother or inspire me.
  • 1 this song catches my attention due to disliking it. I will go out of my way to stop it from playing. i set up my stations to never call for those again.

I am looking for other ways to interface with this to be able to rate songs a little easier/safer (while driving?)

I am hopeful i will have the wiggle room to donate to navidrome, feishin, snapcast, mopidy, spindle, soon!!!!

20
1
submitted 2 months ago* (last edited 2 months ago) by poVoq@slrpnk.net to c/selfhosting@slrpnk.net


wanderer is a self-hosted trail database. Save your adventures!

21


So, I tried to install lidarr on my windows machine via the exe on the website, but my antivirus flagged it immediately. I am sure i could just work around this by disabling the antivirus for a bit or by composing it manually, but for all I know maybe someone inserted some malicious code. Is this an issue y'all have noticed? How can I tell if this is actually malicious?

22
23


I'm considering running Stirling PDF. In a way, it's pretty niche: a tool for editing PDF files. On the other hand, when the need arises every now and then, for myself or those around me, it's always a bit of a pain to figure out how to do it right on Linux.

Stirling seems to be a decent solution for this.

However, seeing things like this in the docs is giving me pause :

Before configuring OAuth 2.0 SSO, ensure you have:

  • Stirling PDF with login enabled (security.enableLogin: true)
  • Valid license for Professional tier or higher

Requirements:

  • Java 21+
  • Linux/Unix system
  • 2GB RAM minimum
  • LibreOffice, Tesseract (for features)

Have some of you deployed it and used it? What's your take?

Thanks!

24


cross-posted from: https://programming.dev/post/51407459

Check what can you use and at what rate of token per seconds would it be... It has examples of many models and quantization levels. Huge resource!

25
view more: next ›